6 min read

Vulnerability in Ivanti Endpoint Manager Mobile Could Allow for Unauthorized Access to API Paths

Vulnerability in Ivanti Endpoint Manager Mobile Could Allow for Unauthorized Access to API Paths

Published 08/31/2023

I. Targeted Entities

  • Ivanti Users

II. Introduction

Norwegian authorities recently revealed a critical zero-day vulnerability in Ivanti Endpoint Manager Mobile (EPMM), posing a significant security threat. The flaw allows unauthenticated remote attackers to bypass authentication and access the server’s API, potentially leading to data theft and unauthorized system modifications.

III. Additional Background Information

On July 24th, the Norwegian Government Security and Service Organization (DSS) and the Norwegian National Security Agency (NSM) informed the public about a zero-day vulnerability in Ivanti Endpoint Manager Mobile (EPMM), a mobile management software that can be used for mobile device management and mobile application/content management (Tenable). This vulnerability has a maximum CVSS score of 10, indicating it is very easy to exploit and requires no specialized tools or skills (Mnemonic).

This vulnerability, classified as CVE-2023-35078, is an authentication bypass in Ivanti’s EPMM. An unauthenticated remote attacker could exploit this vulnerability to access the server’s application programming interface (API), which is normally accessible only to authenticated users (Tenable). Successful exploitation would allow an attacker to be able to access “specific API paths”. By using these unrestricted API paths, a malicious actor could steal personally identifiable information (PII), such as names, phone numbers, and other mobile device details. An attacker can also make other configuration changes, including creating an EPMM administrative account on the server that can further modify a vulnerable system (CISA). The attack consists of changing the URI path to the API v2, which can, in fact, be accessed without any authentication methods (Mnemonic). According to the API documentation, all API calls use the URL format https://[core-server]/api/v2/. If we add the path to a vulnerable endpoint, it is easy to execute commands without needing authentication, as shown here: https://[core-server]/vulnerable/path/api/v2. Luckily, it is fairly simple to detect whether the vulnerability has been exploited in a system. This can be done by checking the logs from the mobile management software to determine if the API v2 endpoint in Ivanti’s EPMM has been targeted (Uzun). This may be evident if regular API calls to unusual paths are present in the logs.

Ivanti reported that the vulnerability impacts all supported versions – Version 11.4 releases 11.10, 11.9 and 11.8. Older unsupported versions/releases are also at risk (CISA). Furthermore, the company has promptly issued security patches for the EPMM vulnerability. Customers can fix it by upgrading the software to EPMM versions 11.8.1.1, 11.9.1.1, and 11.10.0.2. These fixed versions also cover unsupported and End-of-Life (EoL) software versions that are lower than 11.8.1.0 (Uzun).

According to the articles posted by Ivanti, the vulnerability was exploited in the wild as a zero-day against a small number of customers (Tenable). However, it is known that the unnamed attackers utilized this flaw to compromise 12 government ministries in Norway (Muncaster).

IV. MITRE ATT&CK

  • T1190 – Exploit Public-Facing Application
    Adversaries may attempt to exploit a weakness in an Internet-facing host or system to initially access a network. The weakness in the system can be a software bug, a temporary glitch, or a misconfiguration. Exploited applications are often websites/web servers, but can also include databases (such as SQL), standard services (such as SMB or SSH), network device administration and management protocols (such as SNMP and Smart Install), and any other system with Internet-accessible open sockets. Depending on the flaw being exploited, this may also involve Exploitation for Defense Evasion.
  • T1059 – Command and Scripting Interpreter
    Adversaries may abuse command and script interpreters to execute commands, scripts, or binaries. These interfaces and languages provide ways to interact with computer systems and are common across many platforms. Most systems come with built-in command-line interfaces and scripting capabilities; for example, macOS and Linux distributions include a flavor of Unix Shell, while Windows installations include the Windows Command Shell and PowerShell.
  • T1018 – Remote System Discovery
    Adversaries may attempt to obtain a list of other systems on a network by IP address, hostname, or other logical identifier that may be used for Lateral Movement from the current system. Functionality could exist within remote access tools to enable this, but utilities available on the operating system could also be used, such as Ping or Net View.
  • T1015.003 -Server Software Component: Web Shell
    Adversaries may backdoor web servers with web shells to establish persistent access to systems. A Web shell is a Web script hosted on an openly accessible Web server that allows an adversary to use the server as a gateway into a network. A Web shell may provide a set of functions to execute or a command-line interface on the system that hosts the Web server.
  • T1070 – Indicator Removal
    Adversaries may clear Windows Event Logs to hide intrusion activity. Windows Event Logs are a record of a computer’s alerts and notifications. There are three system-defined sources of events: System, Application, and Security, with five event types: Error, Warning, Information, Success Audit, and Failure Audit.
  • T1005- Data from Local System
    Adversaries may search local system sources, such as file systems, configuration files, or local databases, to find files of interest and sensitive data prior to Exfiltration.
  • T1572 – Protocol Tunneling
    Adversaries may tunnel network communications to and from a victim system within a separate protocol to avoid detection/network filtering and/or enable access to otherwise unreachable systems. Tunneling involves explicitly encapsulating a protocol within another. This behavior may conceal malicious traffic by blending in with existing traffic and/or provide an outer layer of encryption (similar to a VPN). Tunneling could also enable the routing of network packets that would otherwise not reach their intended destination, such as SMB, RDP, or other traffic that would be filtered by network appliances or not routed over the Internet.
  • T1090 – Proxy (Internal Proxy)
    Adversaries may use a connection proxy to route network traffic between systems or to act as an intermediary for network communications to a command-and-control server, thereby avoiding direct connections to their infrastructure. Many tools exist that enable traffic redirection through proxies or port redirection, including HTRAN, ZXProxy, and ZXPortMap. Adversaries use these types of proxies to manage command-and-control communications, reduce the number of simultaneous outbound network connections, provide resilience in the face of connection loss, or ride over existing trusted communication paths between victims to avoid suspicion. Adversaries may chain together multiple proxies to further disguise the source of malicious traffic.

V. Recommendations

  • Establish and Maintain a Vulnerability Management Process: Establish and maintain a documented vulnerability management process for enterprise assets. Review and update documentation annually, or when significant enterprise changes occur that could impact this Safeguard.

  • Establish and Maintain a Remediation Process: Establish and maintain a risk-based remediation strategy documented in a remediation process, with monthly or more frequent reviews.

  • Perform Automated Application Patch Management: Apply updates to enterprise assets through automated patch management on a monthly or more frequent basis.

  • Perform Automated Vulnerability Scans of Internal Enterprise Assets: Perform automated vulnerability scans of internal enterprise assets on a quarterly or more frequent basis. Conduct both authenticated and unauthenticated scans, using a SCAP-compliant vulnerability scanning tool.

  • Remediate Detected Vulnerabilities: Remediate detected vulnerabilities in software through processes and tooling on a monthly or more frequent basis, based on the remediation process.

  • Ensure Network Infrastructure is Up-to-Date: Keep network infrastructure up-to-date. Example implementations include running the latest stable software release and/or using currently supported network-as-a-service (NaaS) offerings. Review software versions monthly or more frequently to verify support.

  • Establish and Maintain a Penetration Testing Program:  Establish and maintain a penetration testing program appropriate to the enterprise's size, complexity, and maturity. Penetration testing program characteristics include scope, such as network, web application, Application Programming Interface (API), hosted services, and physical premise controls; frequency; limitations, such as acceptable hours, and excluded attack types; point of contact information; remediation, such as how findings will be routed internally; and retrospective requirements.

  • Manage Default Accounts on Enterprise Assets and Software: Perform periodic external penetration tests, at least annually, in accordance with program requirements. External penetration testing must include enterprise and environmental reconnaissance to detect exploitable information. Penetration testing requires specialized skills and experience and must be conducted through a qualified party. The testing may be a clear box or an opaque box.

  • Remediate Penetration Test Findings: Remediate penetration test findings based on the enterprise’s policy for remediation scope and prioritization.

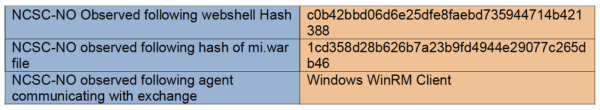
VI. IOCs (Indicators of Compromise)


VIII. References

Mnemonic. (2023, July 25). Advisory: Ivanti Endpoint Manager Mobile (EPMM) Authentication Bypass Vulnerability. https://www.mnemonic.io/resources/blog/ivanti-endpoint-manager-mobileepmm-authentication-bypass-vulnerability/

Tenable®. (2023, July 25). CVE-2023-35078: IVaNti Endpoint Manager Mobile (EPMM) / MobileIron Core Unauthenticated API Access vulnerability. https://www.tenable.com/blog/cve-2023-35078-ivanti-endpoint-managermobile-epmm-mobileiron-core-unauthenticated-api-access

Uzun, T. (2023, July 25). A critical zero-day in Ivanti EPMM (Formerly MobileIron Core) is actively exploited (CVE-2023-35078). SOCRadar® Cyber Intelligence Inc. https://socradar.io/critical-zero-day-in-ivanti-epmm-formerly-mobileiron-core-isactively-exploited-cve-2023-35078/

Cybersecurity and Infrastructure Security Agency CISA. (2023, July 24). Ivanti releases a security update for Endpoint Manager Mobile (EPMM) addressing CVE-2023-35078. https://www.cisa.gov/news-events/alerts/2023/07/24/ivanti-releases-securityupdates-endpoint-manager-mobile-epmm-cve-2023-35078

Muncaster, P. (2023, July 25). Ivanti patches a Zero-Day bug used in attacks in Norway. Infosecurity Magazine. https://www.infosecurity-magazine.com/news/ivantipatches-zeroday-bug-norway/

Uzun, T. (2023, August 4). A critical zero-day in Ivanti EPMM (formerly MobileIron Core) is actively exploited (CVE-2023-35078). SOCRadar® Cyber Intelligence Inc. https://socradar.io/critical-zero-day-in-ivanti-epmm-formerly-mobileiron-core-isactively-exploited-cve-2023-35078/

Contributing Security Analysts: Nahyan Jamil, Erika Delvalle, Alessandro Lovadina, Sreten Dedic, EJ Bulut, Uday Bilakhiy, Yousef Blassy.

Other posts of interest...

Zero-Day Vulnerability in MOVEit

1 min read

Zero-Day Vulnerability in MOVEit

Published 06/23/2023 I. Targeted Entities MOVEit Customers II. Introduction A critical SQL injection vulnerability has been discovered in MOVEit, a...

Read More
Microsoft Releases Workaround for Zero-Day Flaw

1 min read

Microsoft Releases Workaround for Zero-Day Flaw

Originally published: 06/16/2022 I. Targeted Entities Microsoft Office users II. Introduction Microsoft has recently established a workaround for a...

Read More
Google Patches Exploited Chrome Bug

1 min read

Google Patches Exploited Chrome Bug

Originally published 07/14/2022

Read More